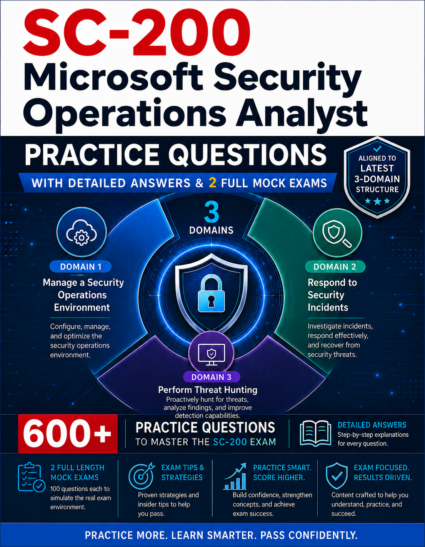
Study Guide : Exam Prep Book with Microsoft Sentinel, Defender XDR & KQL Scripting
Prepare for the Microsoft SC-200 Security Operations Analyst certification with a comprehensive study guide covering Microsoft Sentinel, Defender XDR, KQL, incident response, threat hunting, and modern security operations concepts.
Prepare for the Microsoft SC-200 Security Operations Analyst certification with a structured study guide designed to build both exam knowledge and practical security operations skills.
This CogniSkill study guide covers key security operations concepts and technologies including Microsoft Sentinel, Microsoft Defender XDR, incident investigation and response, threat hunting, and Kusto Query Language (KQL).
Rather than focusing only on memorization, the book connects certification concepts with practical security operations scenarios to help learners understand how Microsoft security technologies can be used to investigate threats, respond to incidents, and strengthen security operations.
BOOK DETAILS
Prepare with confidence
What you’ll learn
Understand core Microsoft security operations concepts
Work with Microsoft Sentinel for security monitoring and investigation
Understand Microsoft Defender XDR security operations capabilities
Investigate and respond to security incidents
Apply threat-hunting concepts and techniques
Use KQL concepts for security investigation and analysis
Understand alerts, incidents, and security data
Apply security operations knowledge to practical scenarios
Prepare for the major knowledge areas assessed by the SC-200 exam
What’s inside
Comprehensive SC-200 concept coverage
Microsoft Sentinel concepts and workflows
Microsoft Defender XDR coverage
Incident investigation and response guidance
Threat-hunting concepts
KQL scripting and query concepts
Practical security operations scenarios
Exam-focused explanations and preparation
Review material for major SC-200 knowledge areas
Who this book is for
IT professionals preparing for the Microsoft SC-200 exam
Security operations analysts
SOC analysts and aspiring SOC professionals
Cybersecurity professionals working with Microsoft security technologies
Microsoft Sentinel and Defender users
IT support professionals transitioning into security operations
Learners seeking practical Microsoft security operations knowledge
COGNISKILL BOOKS
Continue Your Microsoft SC-200 Preparation
Explore other CogniSkill books for the same certification.